The core systemsbehind regulatedfinancial operations.
Qirin X builds the back-office systems compliance, operations and risk teams run every day. Built by compliance and risk practitioners: regulation is encoded as rules the system runs.
- one sign-in
- one database
- audit trail
- row-level security
Every obligation becomes a rule the system enforces.
Approval routes, review cycles, retention and four-eyes control live in the system and the database, not in e-mail or on screen. Scroll through six of them.

Enforced in the database, not on screen.
row-level security · every business table
retention lock · edit and delete refused
sign-ins · logged with time and IP1 Core System
One platform, one sign‑in, three modules — bought together or one at a time.
- one sign-in
- roles and permissions
- audit trail
- Thai / English
- scheduled jobs
- secure file exchange with external systems
- KYC Core
The customer-facing onboarding journey, white-labelled under the institution's own brand and domain.
- CDD Corealso sold on its own
The officer console for customer due diligence — one screen for every officer role.
- Agent Core
Commission and retention for sales, RMs, investment consultants and freelance agents.
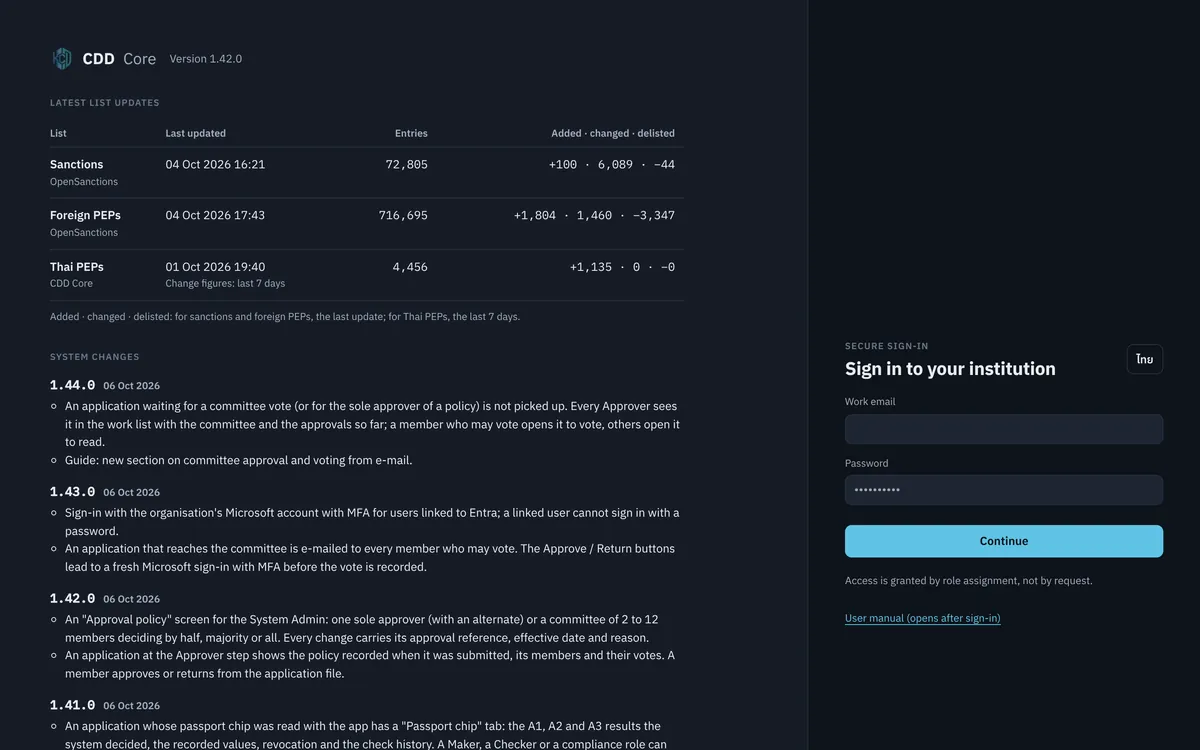
One sign-in, with list status on the first screen
01 / 06The sign-in page shows when the Sanctions and PEP lists were last updated, and what changed in the system, before work starts.
Already have onboarding? Buy CDD Core alone and connect it to the customer source you already have.
CDD Core connects to the institution's existing customer source by file or API and owns only the outputs of CDD work — risk, screening, reviews, filings. It is a customer index, not a second customer master.
- risk
- screening
- reviews
- filings
Risk Core
One platform for the whole risk life cycle — identify, assess, monitor, respond, recover. Built for Thai corporate groups and the subsidiaries inside them, from the risk register to the employee's phone.
- Down-Only Visibility
A parent sees downward only; siblings never see each other.
- Subsidiary-Independence
A parent reads but never acts; the database refuses, not just the screen.
- Report-Up-Only
Data flows up to the parent only; no arrow between siblings.
- Reported-Then-Visible
An item becomes visible to the parent only once it has been reported.
ERM Core — the risk desk
Risk register, loss events, KRIs and BIA for every company in the group, rolled up into one view.
See how ERM Core works →- RCSA
A risk register per entity, scored likelihood × impact against a group-owned criteria set — computed, never typed.
- Loss Event
Mapped to Basel event types, gross / recovered / net, with materiality tiers routed automatically.
- KRI
Versioned threshold bands, observations, and trend and breach views.
- BIA
Critical activities with MTPD, RTO and RPO and a computed criticality tier, approved and versioned.
- Dashboards
Executive summary per entity, group roll-up and loss report pack, in Thai and English.
BCP Core — every employee's phone
Hazard watch, early warning, check-in and call tree, ready the moment an incident starts.
See how BCP Core works →- Hazard watch
Live feeds for weather, water level, earthquake and air quality, with early warning by push.
- BCP level
Normal · Standby · Activated · Closed, pushed to every phone on every change.
- Check-in
One tap — safe, affected, need help — with a live status map and a call tree built from the organisation structure.
- Exercise
An exercise log, and an incident becomes a loss event without re-keying.
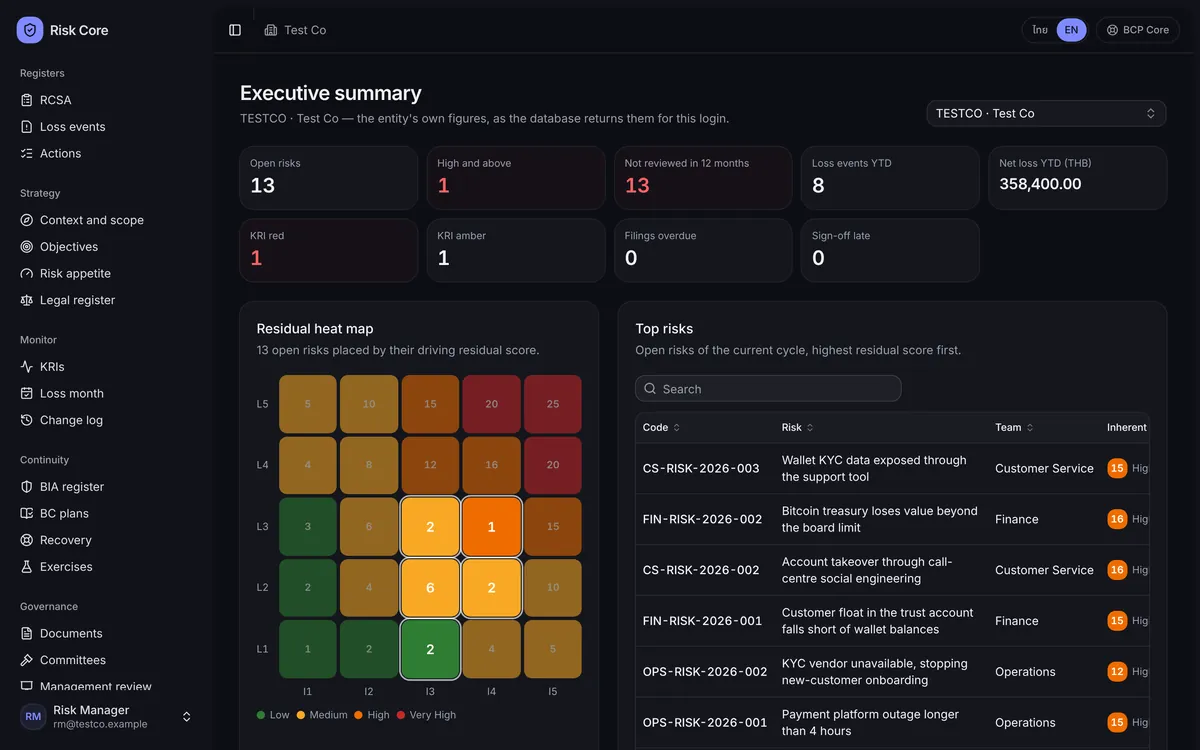
The whole company's risk on one page
01 / 05Open risks, loss events, KRI status and the residual heat map, all drawn from each team's risk register.
For financial groups
Lead with group hierarchy, consolidated reporting, Basel-mapped losses, built to serve COSO ERM (2017) and ISO 22301.
For corporates & SMEs
Lead with BCP Core — early warning, check-in, status map, call tree — then ERM Core as the layer to grow into.
Modular: ERM Core only, BCP Core only, or both on one core · pricing: contact us
Built to serve COSO ERM (2017) and ISO 22301; loss events map to the Basel operational-risk event taxonomy · designed for companies supervised by SEC, BOT and OIC
Trading Core
OTC desk and back office for digital‑asset dealers — from RFQ and the trade blotter to hedge tickets, four‑eyes reversal and SEC e‑Reporting. Follow one trade along the path.
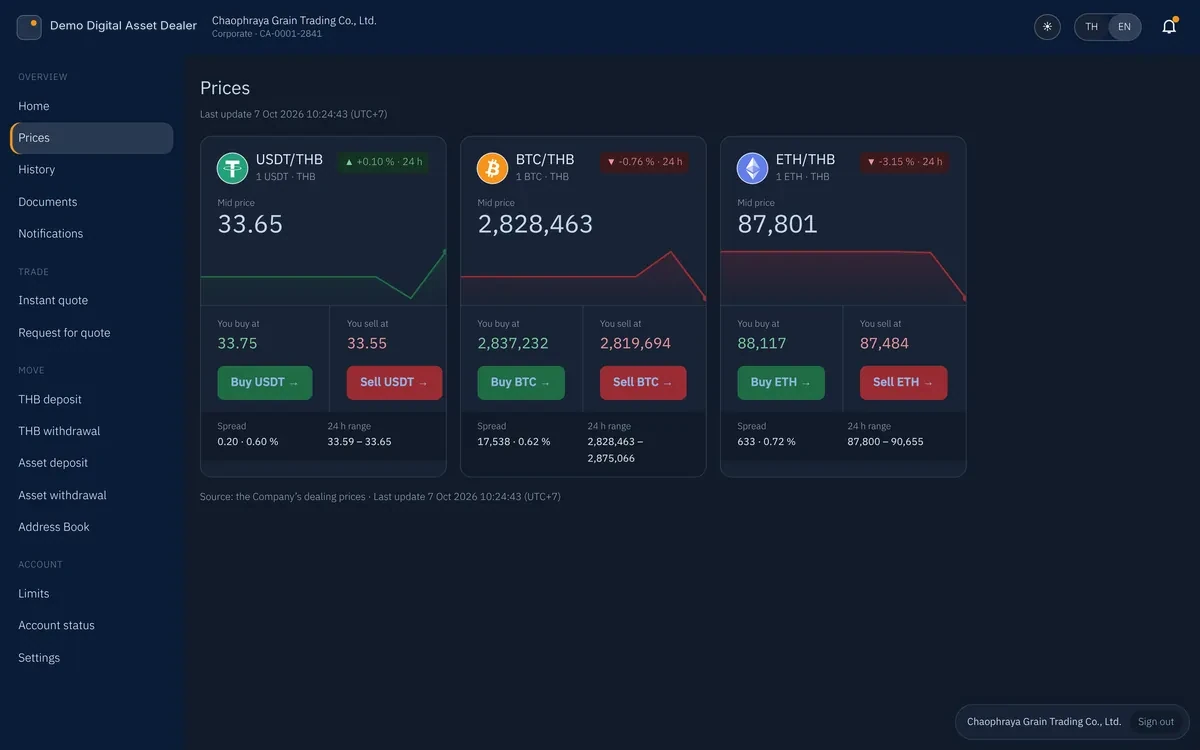
Customers see BTC, ETH and USDT prices
01 / 07Home, Prices, Instant quote and Request for quote: every order lands in the same blotter the dealer sees.
Security by design.
Access rules are enforced in the database, not only on screen, on infrastructure encrypted at rest and in transit.
- Screennot the only check
what a user sees and clicks
- Data layerrole checks
rights checked by role in the data layer · one active session per user · idle sign-out set by the institution
- Databaserules enforced here
row-level security on every business table · records under retention: edit and delete refused · append-only history · audit log of every action
- InfrastructureSingapore · AWS ap‑southeast‑1
managed PostgreSQL · AES-256 at rest · TLS in transit · backed up daily · HTTPS on every site · atomic deploys, instant rollback
Both products
- Row-level security enforced in the database
- Role checks in the data layer, not only on screen
- Audit log of every action: who and when
1 Core System
- Institutions separated by row-level security on every business table
- One active session per user; idle sign-out set by the institution
- Every sign-in and refused sign-in logged with time and IP
- Records under retention cannot be edited or deleted; the database refuses
Risk Core
- Each company's data separated by row-level security, including companies of the same group; a separate database per company on request
- Group view by report-up only: a parent receives what each subsidiary has approved
- MFA for everyone: password plus authenticator code
- Append-only history for valuations, submissions and the audit log


Technology
The stack, in the open.
1 Core System, Risk Core and Trading Core run on one stack. The rules live in the database, and the data sits in PostgreSQL, an open-source standard rather than a format only one vendor can read.
Why it matters
Rules run in the database, so every screen, API call and scheduled job obeys the same rule.
Where data lives
Customer records are stored in Singapore. Web screens are static: no customer record passes through the web host.
Engineering
Source in GitHub with automated checks on pull requests. Docs built with Astro Starlight. Sub-processors →
Built for regulated back offices.
- Asset management companies
- Fund selling agents
- Securities firms
- Digital-asset businesses
- Payment service providers
- Digital service platforms (DSP)
- Any organisation that needs a smart back office
Why QX
- Built by compliance and risk practitioners — regulation is encoded as rules the system runs.
- Every decision is recorded with who, when and why.
- Delivered in sessions, with the client's staff testing each one (UAT) before go-live.
Designed by a practising Head of Risk with 15+ years in Thai capital markets, fintech and digital-asset GRC, including SEC Thailand licensing work.
We publish how the systems work, including who they fit and who they do not, down to controls and integrations. Who it is for →
Partners
Consultant to the development of Risk Core and 1 Core System
See the rules run on your own cases.
Tell us whether it is 1 Core System, CDD Core on its own, Risk Core or Trading Core. We will set up a demo session with your team.